Practical insights on cybersecurity, managed IT services and infrastructure to help your business reduce risk and operate with confidence.
Schedule an IT Risk Assessment
September 30, 2026
A client recently lost money to a scam that a firewall was never going to catch. The story is worth telling in detail, since every technical control in that client’s environment worked exactly as intended. The attack did not break through the network. Instead, it walked in through a phone call, and the only control […]
Read Post
September 15, 2026
Nobody sets out to waste money on Microsoft 365 licensing. It happens gradually. Someone leaves the company, and their license sits untouched, generally without anyone noticing right away. A project wraps up and the Power BI seat assigned for it never gets removed. A new hire gets the wrong SKU from the start, and nobody, […]
Read Post
September 8, 2026
Most businesses have spent real money making sure a server failure will not stop operations. Backups exist, cloud platforms replicate data and disaster recovery plans sit ready for exactly that scenario. Then a single cable running into the building stays the one thing nobody planned around. Microsoft 365, VoIP phones, hosted line-of-business applications and cloud […]
Read Post
September 3, 2026
A green checkmark next to a backup job means, at minimum, that the job ran. It does not mean the data inside it can actually come back. That gap between a completed backup and a working backup is where a lot of businesses get a bad surprise. Often at the worst possible moment, once their […]
Read Post
August 26, 2026
Most conversations about cybersecurity focus on a single tool or a single incident, when the real picture is much bigger. A strong cybersecurity risk posture is based on five distinct pieces.
Read Post
August 19, 2026
SMS phishing gets attention. Fake Teams invites get attention. However, email security technology still matters more than either. Learn why email remains the most common way an attacker gains a foothold in a client network.
Read Post
August 12, 2026
Most new clients do not find us through a Google search. They find us because someone they trust told them to call, and that carries more weight than any ad or search result ever could.
Read Post
August 5, 2026
Evaluating a managed IT provider is harder than it looks. Most MSPs answer the same questions with the same language. They all promise proactive support, responsive service and a long-term partnership. Find out which questions to ask an MSP, and what honest answers actually sound like.
Read Post
July 29, 2026
Mergers and acquisitions are supposed to make a business stronger. New leadership, expanded resources and broader capabilities should improve operations across the board. However, IT stability after an acquisition is one of the first things to erode.
Read Post
July 22, 2026
A handful of our clients are family-owned and operated, several of them in warehousing and freight and logistics. Working with them has, in practice, taught us something that does not show up in a typical MSP sales pitch.
Read Post
July 15, 2026
Most IT support interactions end the same way. The ticket closes, the technician moves on and the client never hears another word about it. For many providers, that silence is the standard.
Read Post
July 8, 2026
IT ticketing and documentation are the operational infrastructure that separates a mature managed services provider from one that handles each problem as if it has never seen anything like it before.
Read Post
July 1, 2026
For organizations that already have an internal IT person, the better question to ask an MSP is how to make that person significantly more capable without replacing them.
Read Post
June 23, 2026
Is an MSP worth it compared to calling someone when something breaks? It is a fair question, and CFOs and COOs ask it regularly. The monthly fee is visible on a budget line. However, the value of what that fee prevents is largely invisible.
Read Post
June 12, 2026
This guide answers the questions business leaders ask most often before making that decision: whether to hire in-house or use an MSP, how co-managed IT actually works, what to ask during an evaluation, how to recognize good value and what mistakes to avoid.
Read Post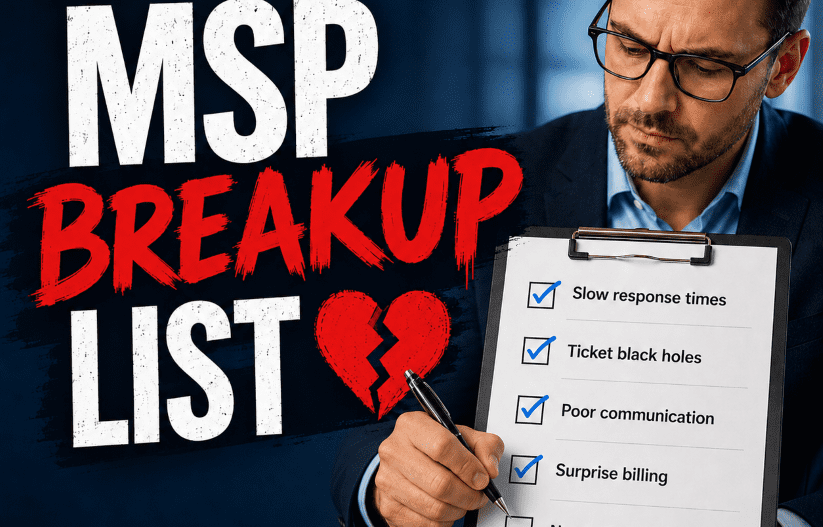
June 4, 2026
At STF Consulting, we built our model specifically around the gaps clients told us they experienced. This post covers the seven MSP problems we hear most often and the specific ways we approach each one differently.
Read Post
May 26, 2026
Technical controls can be well-designed and still fail to deliver lasting outcomes when the business relationship behind them lacks shared ownership. This is a people and process problem, not a technology problem.
Read Post
May 18, 2026
Standardization is not about limiting options for their own sake. It means committing to a defined set of technologies the team has fully evaluated, genuinely understands and can manage with depth and confidence.
Read Post
May 13, 2026
This guide covers which model to use for which task, what the Claude Team plan adds for organizations and the specific guardrails that need to be in place before Cowork or Claude Code touches your files or network.
Read Post
May 11, 2026
This guide covers all three, along with how STF Consulting helps organizations adopt AI productively without creating security and governance risks in the process.
Read Post
May 4, 2026
A managed service provider is a company that takes ongoing responsibility for a defined set of IT systems and services on behalf of another organization. An MSP does not show up when something breaks and leave when it is fixed.
Read Post
April 30, 2026
IT spring cleaning is not a metaphor. Every IT environment accumulates hidden risk over time, not from major failures but from small issues that build quietly in the background. They create exposure that compounds until something forces the issue.
Read Post
April 22, 2026
A weak email security strategy remains one of the most reliable red flags we uncover during IT onboarding. Email is still the most common entry point for attacks, yet the defenses protecting it are often uneven, outdated or tuned so loosely that real threats blend in with legitimate traffic.
Read Post
April 16, 2026
Inconsistent user onboarding and offboarding processes create security gaps that most organizations do not discover until something goes wrong. During IT onboarding, we regularly find that no standardized process governs how teams create or remove user access.
Read Post
April 13, 2026
STF Consulting led a structured transition to OpenVPN, designing and deploying a standardized remote access solution across multiple client environments. The result was a system built for long-term stability.
Read Post
April 8, 2026
Backup validation and resilience are two areas where most organizations carry more risk than they realize. One of the most common red flags we uncover during IT onboarding is a backup strategy that exists on paper but has never been truly tested. Jobs run on a schedule. Someone assumes the data is protected. But nobody […]
Read Post
March 31, 2026
Access accumulates because business priorities shift, staff turns over and IT teams are stretched thin. Each change is small on its own, but the result is a sprawling permissions footprint that nobody fully owns.
Read Post
March 24, 2026
Businesses often purchase laptops, desktops, and accessories as one-off deals. While these decisions may appear cost-effective upfront, they introduce long-term operational risk and increased support costs.
Read Post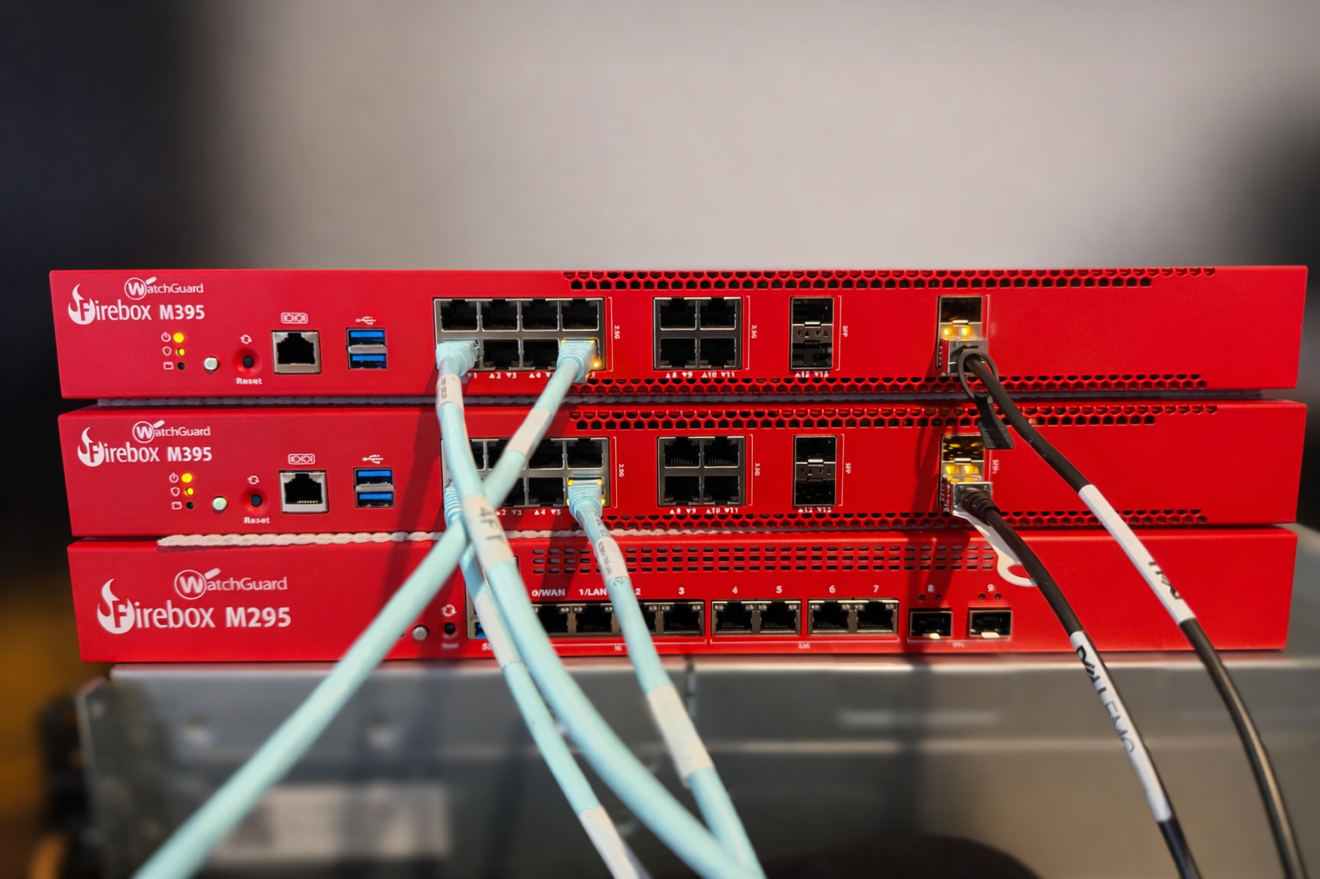
March 19, 2026
This week, the STF Consulting team deployed next generation firewall platforms from WatchGuard, including the Firebox M Series in client environments. Learn why modern hardware platforms are critical.
Read Post
March 11, 2026
The issue with blanket rules is that they prioritize convenience over intent. As environments evolve, those rules remain in place long after their original purpose is forgotten.
Read Post
March 4, 2026
When everything can communicate freely, lateral movement becomes easy. A compromised laptop can quickly lead to access to servers or production systems because nothing is in place to stop it.
Read Post
January 29, 2026
If you’ve ever wondered why some companies bounce back from IT issues without skipping a beat—while others grind to a halt—it usually comes down to one thing: layers. Layers of protection, layers of process, and layers of planning.
Read Post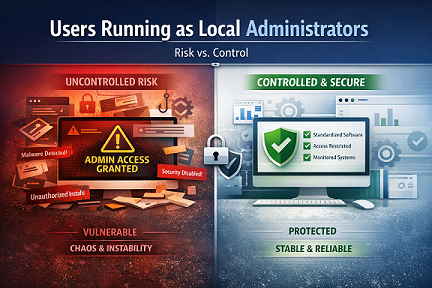
January 29, 2026
Running as a local administrator creates unnecessary exposure across your environment.
When a user has elevated privileges, anything they interact with gains the same level of access. Malware, phishing payloads, browser extensions, and compromised downloads can execute system level changes without restriction.